Office 365 Connector v1.0
25:59
The Office 365 Connector is used to configure SSO using SAML 2.0 with PingFederate.
Related Videos
For "SAML"
-
Play video IdP Discovery
IdP Discovery
Ian Barnett leads a discussion to help understand the common challenge for Service Providers face regarding how to discover the correct Identity Provider for their customer when using SAML and SP initiated workflows.
32:45
-
Play video SSO for SaaS Apps: Customer Onboarding
SSO for SaaS Apps: Customer Onboarding
Once you've SSO-enabled your application in PingOne using REST APIs or SAML, learn how to invite and onboard your customers to your application. There are two recommended ways - the self service widget and an email invitation. We'll cover both.
4:09
-
Play video Identity bridges: AD Connect configuration
Identity bridges: AD Connect configuration
How to configure ADConnect (a lightweight .NET application that will send SAML assertions to PingOne to enable SSO to your applications).
14:54
-
Play video SAML 101
SAML 101
Many businesses use an open standard protocol called SAML to share identities between multiple organizations and applications. SAML enables single sign-on, eliminating most passwords and the risks associated with them. See how it works.
3:37
-
Play video OAuth, PingFederate, and SAML
OAuth, PingFederate, and SAML
Explore how PingFederate can be used to combine SAML with OAuth 2.0. Consider the benefits achieved through the combination of these protocols, and learn how PingFederate can be configured for the OAuth 2.0 SAML Bearer Assertion grant type use case.
52:44
-
Play video How to Configure Issuance Criteria in PingFederate
How to Configure Issuance Criteria in PingFederate
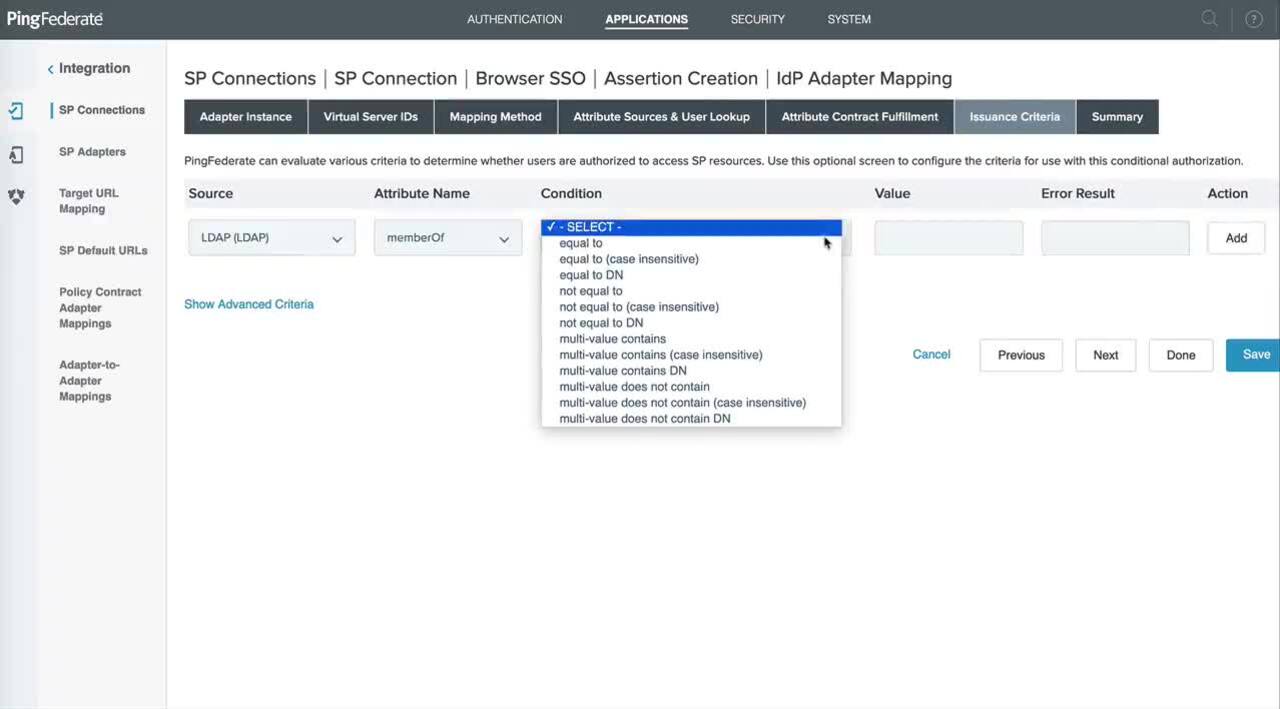
This video provides an overview of issuance criteria, where it can be used in PingFederate, and a demonstration of how to configure issuance criteria from the SAML IdP's perspective.
3:45